Secure AI. Isolated Execution.
Protected Context.
Run every AI agent in its own dedicated virtual machine on Google Cloud. CommandLyne protects enterprise data while keeping personal habits and team knowledge strictly separated.
Ask CommandLyne in plain language to find information, create content, and move work forward across your connected enterprise tools.
Book a Demo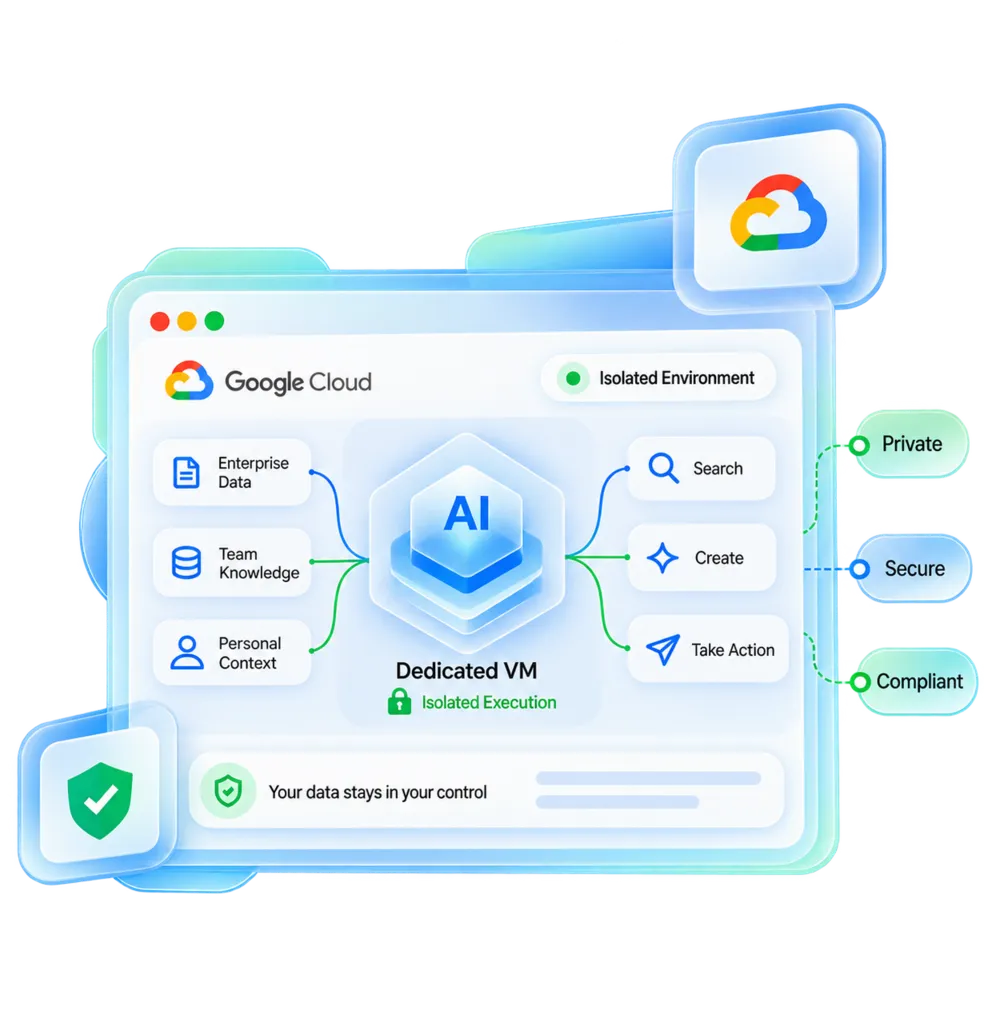
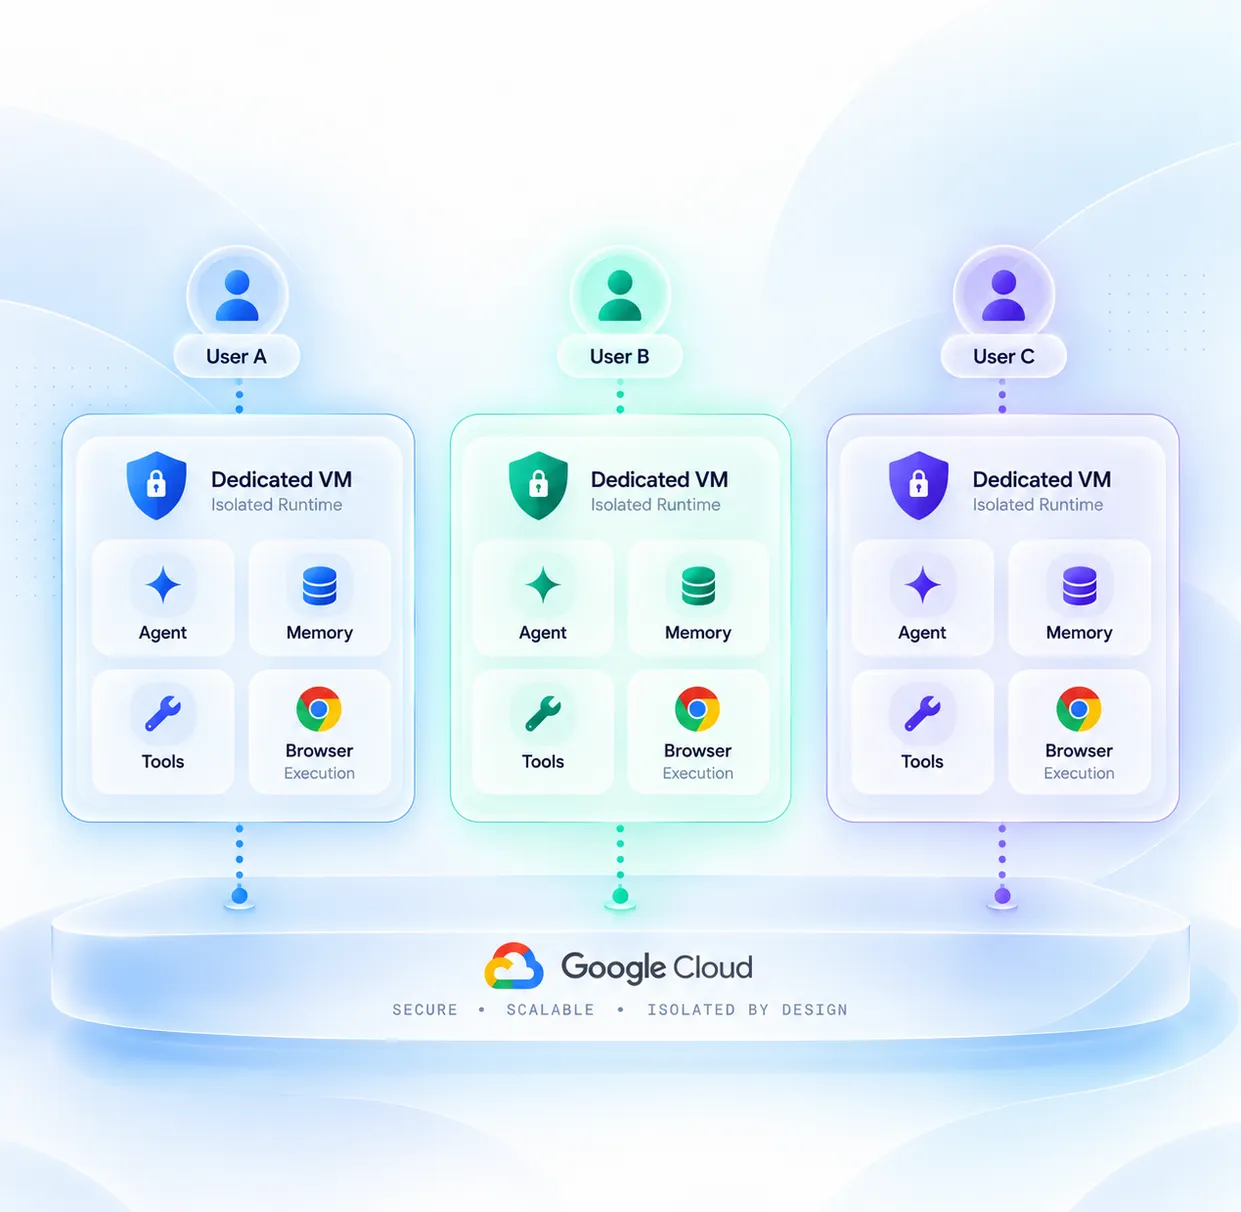
One user. One isolated VM.
Unlike platforms that mix all users into one shared space, CommandLyne gives every agent its own dedicated virtual machine.
Dedicated VMs — Zero shared runtime memory between users.
No Data Leakage — Actions in one session cannot touch another user's workspace.
Safe Automation — Tools and browser tasks execute inside isolated sandboxes.
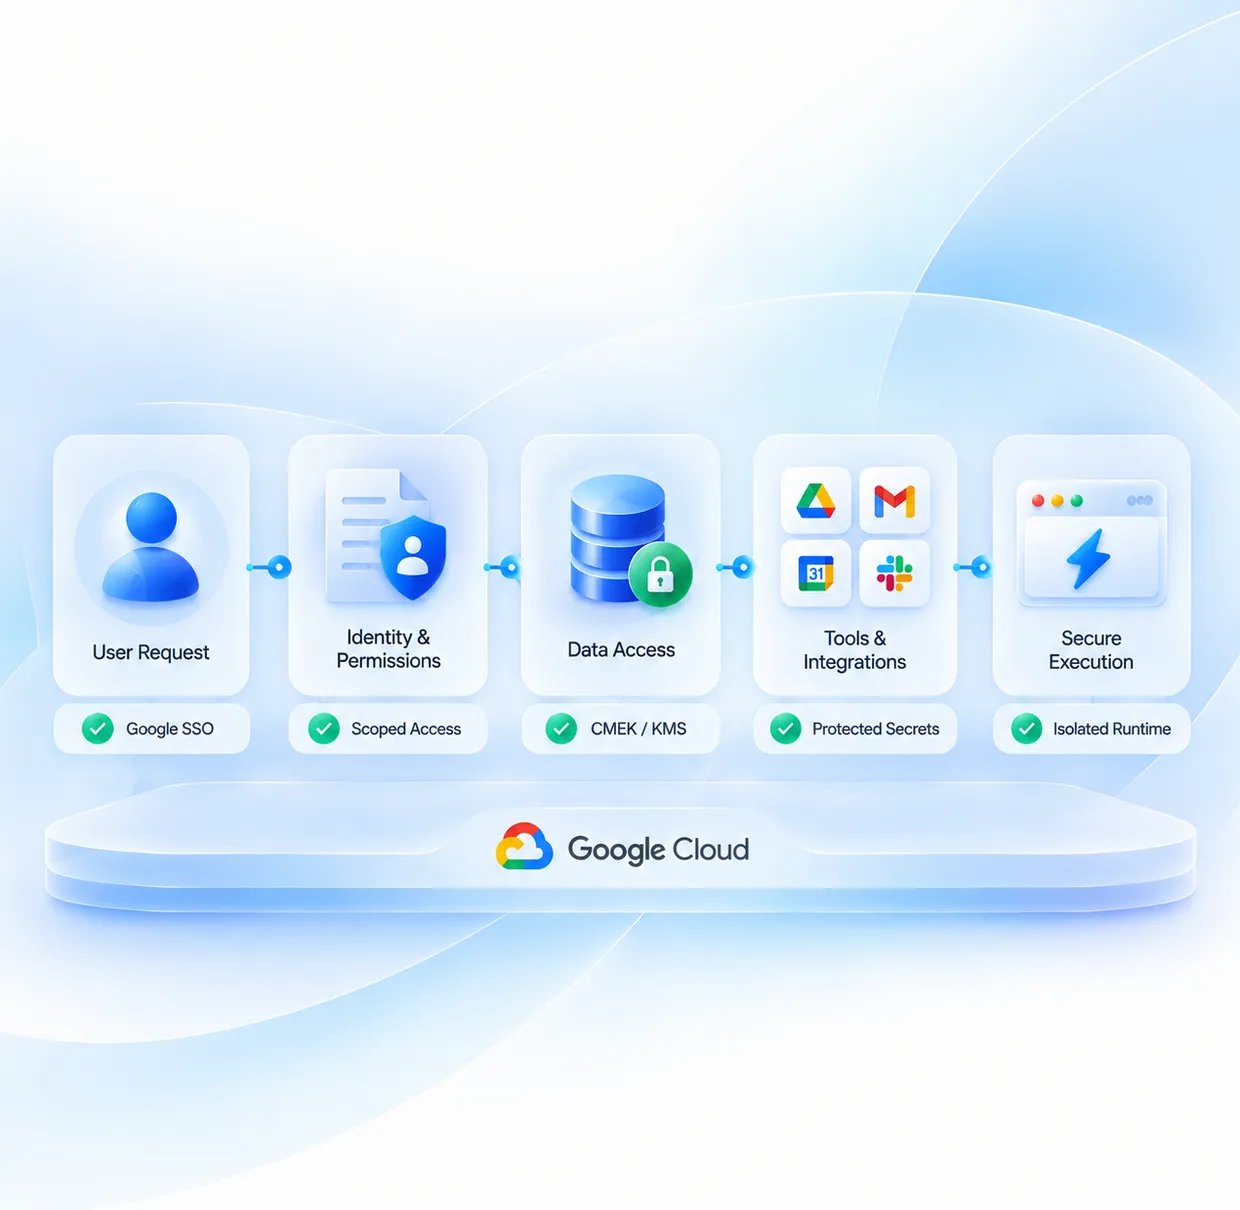
Security built into every action.
Comprehensive controls protect your data from the prompt to final execution.
KMS & CMEK Encryption — Encrypt data using your own Google Cloud keys.
No Plaintext Secrets — Credentials and tokens are never stored unprotected.
Scoped Tool Access — Agents only access the specific tools each task needs.
Google SSO — Native, secure authentication for every user.
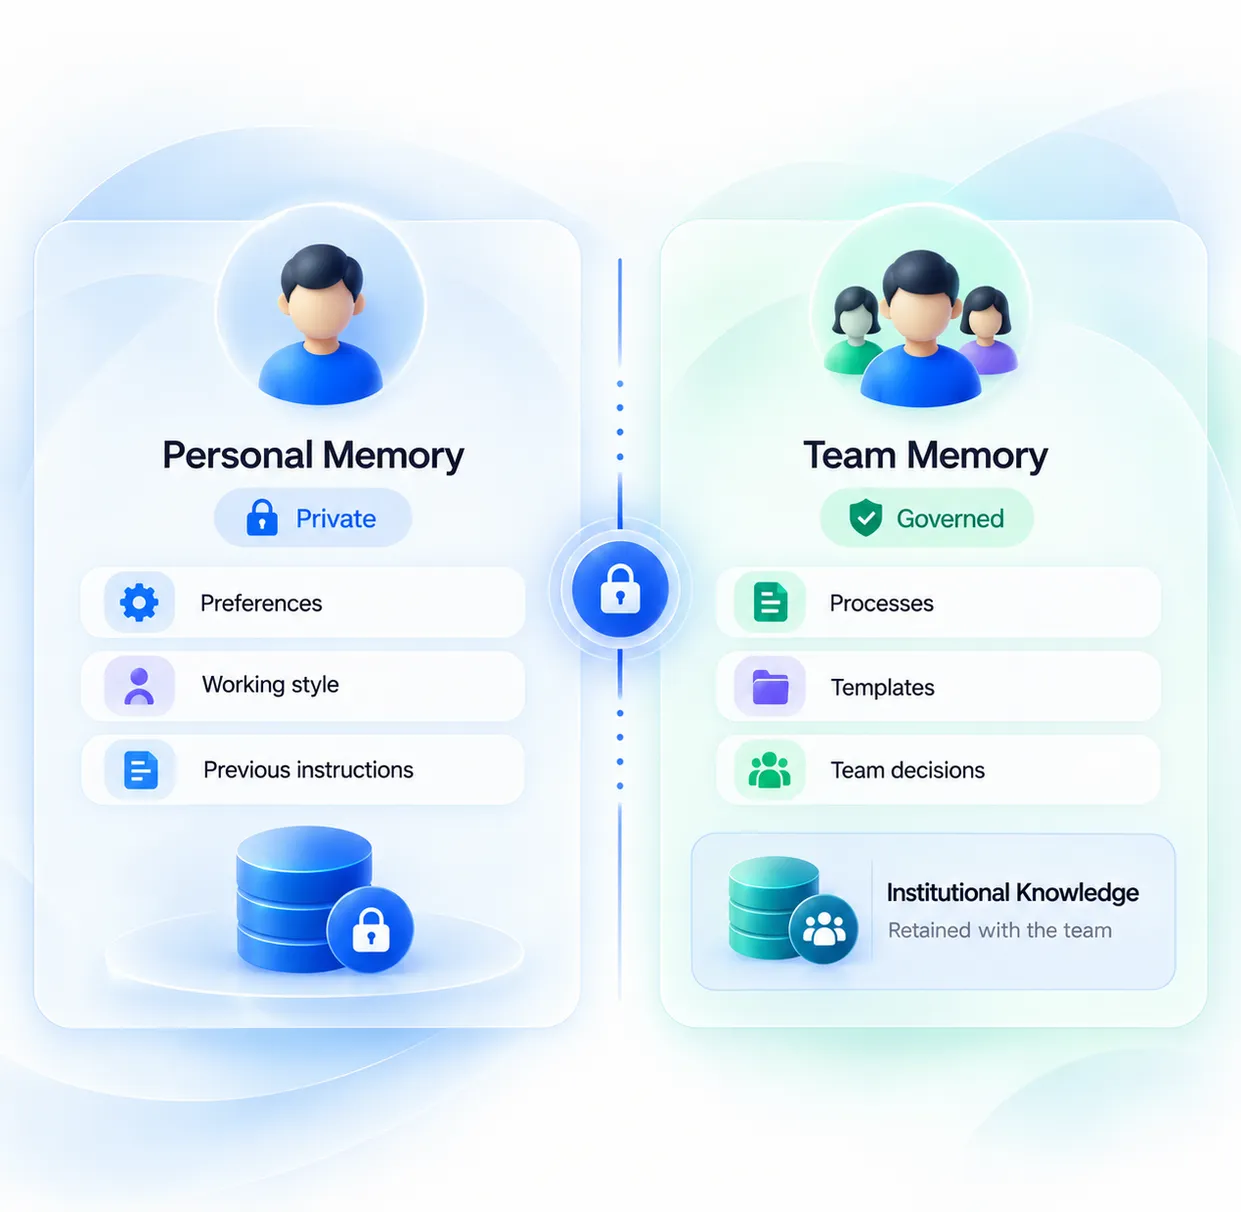
Context that stays where it belongs.
AI remembers how you work without exposing private data to the rest of the company.
Personal Memory (Private) — Keeps your working style and preferences private to you.
Team Memory (Governed) — Shares standard processes, templates, and decisions across authorized teams.
Institutional Continuity — Knowledge stays with the team even when employees leave.
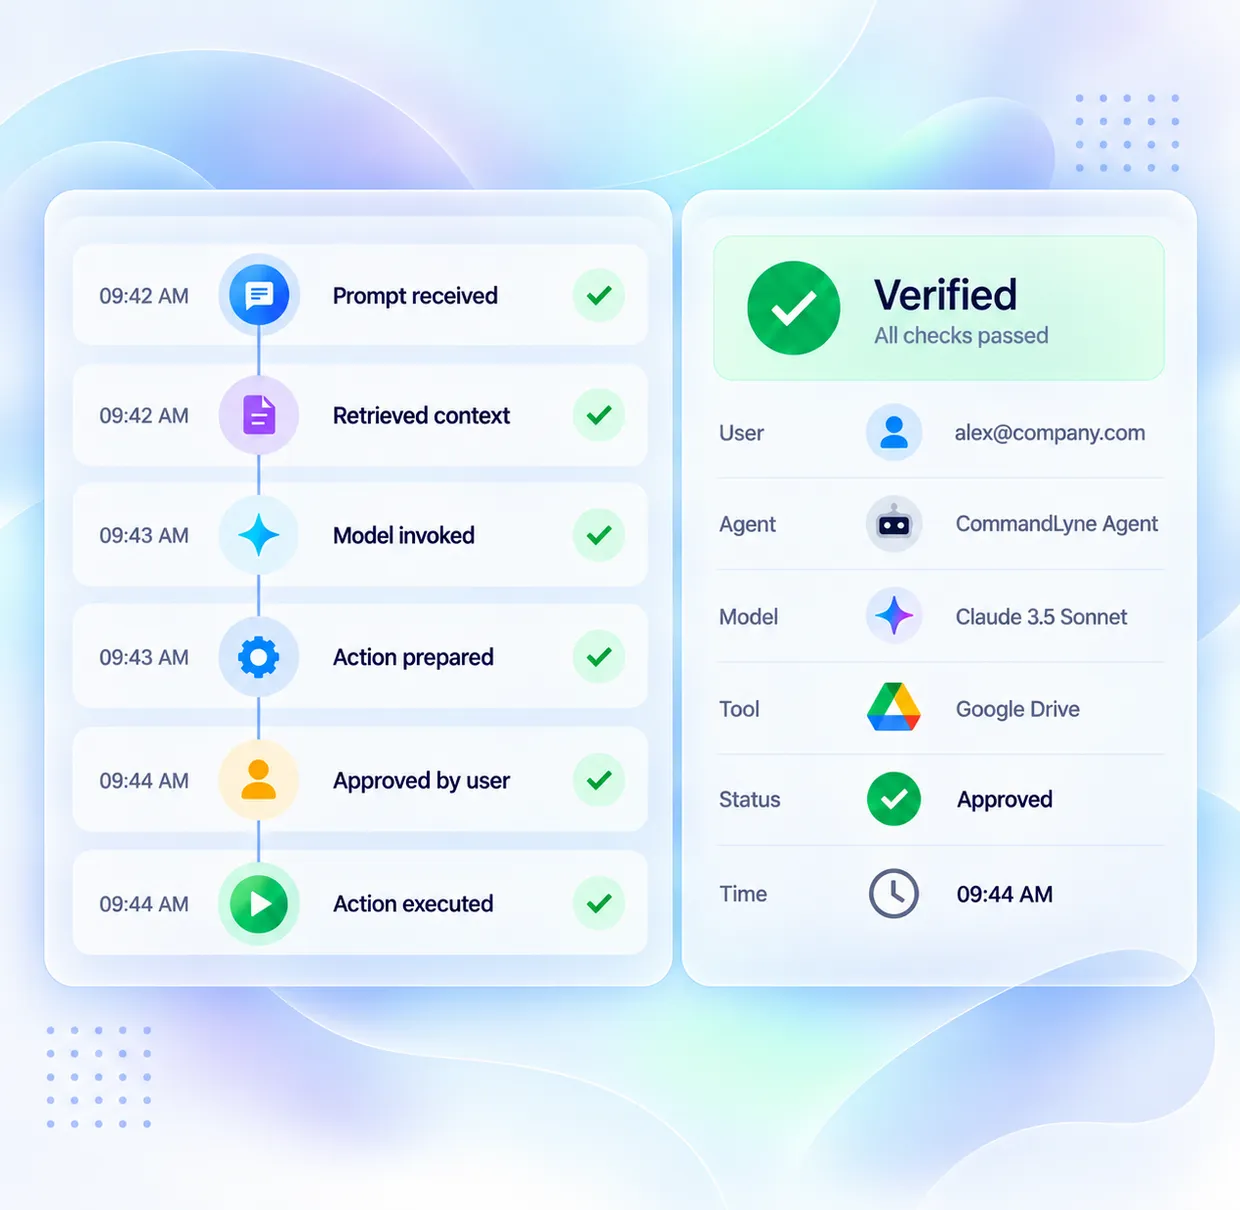
Every AI action logged and verifiable.
Know exactly what your AI accessed, what it executed, and who approved it.
Full Audit Trail — Record every prompt, data query, and tool execution.
Memory Transparency — See what context was retrieved for every answer.
Human Sign-Off — Enforce approvals before sensitive actions execute.
Put enterprise security around every AI action.
Bring VM-level isolation, customer-managed encryption, and governed memory to your organization.